A mid-sized global bank told the security vendor RSA that it had no AI agents. Policy prohibited them, so the answer was simple: zero. Then RSA ran an audit. It found more than 4,000 agents already running loose inside the enterprise.
That number should stop every bank president, practice administrator, and managing partner in Northeast Indiana cold — because the bank wasn't lying. It genuinely believed its policy was reality. According to MarkTechPost's coverage of RSA's September 29 launch event, RSA President and Chief Product & Strategy Officer Jim Taylor put it bluntly: “Agents don't tend to respect policy. We did an audit and found more than 4,000 agents running around in their enterprise.”
If you run a community bank, a credit union, a dental or medical group, a law firm, or an insurance office in Fort Wayne or DeKalb County, this is the story that matters more than any model-release headline. It is not a sci-fi scenario. It is an audit finding at a regulated institution that thought it had the problem handled. Here at Cloud Radix we have been emphasizing that you already have AI agents you can't see — and now a Fortune-grade identity vendor is validating the exact architecture we deploy. Let's break down what RSA announced, why your “no-AI” policy is already false, and the three-step fix a 15-to-200-person regulated shop can actually stand up before its next audit.
Key Takeaways
- RSA announced Agent ID, a three-module platform — Discover, Secure, and Govern — built specifically for regulated industries; Discover and Secure reach general availability November 16, 2026, with Govern following in the first half of 2027.
- In an RSA audit, a bank with a stated “no agents” policy was found running more than 4,000 agents — proof that policy on paper is not the same as control in practice.
- The real failure mode isn't a rogue AI; it's a well-meaning employee plus an over-permissioned agent. One operator asked an agent to “get all the data” and inadvertently took the company's Salesforce instance down.
- IBM's research pins shadow-AI breaches at $670,000 more per incident than the average breach — and finds most affected organizations had no AI access controls at all.
- Regulated Fort Wayne firms face HIPAA, GLBA/FFIEC, and Indiana's breach-notification law — frameworks that may still apply when an AI agent is involved.
- The defensible response scales down to SMB size: discover your agents, put a Secure AI Gateway in front of every tool call, and keep a compliance-mapped audit trail.
What Did RSA Actually Announce — and Why Should a Fort Wayne Firm Care?
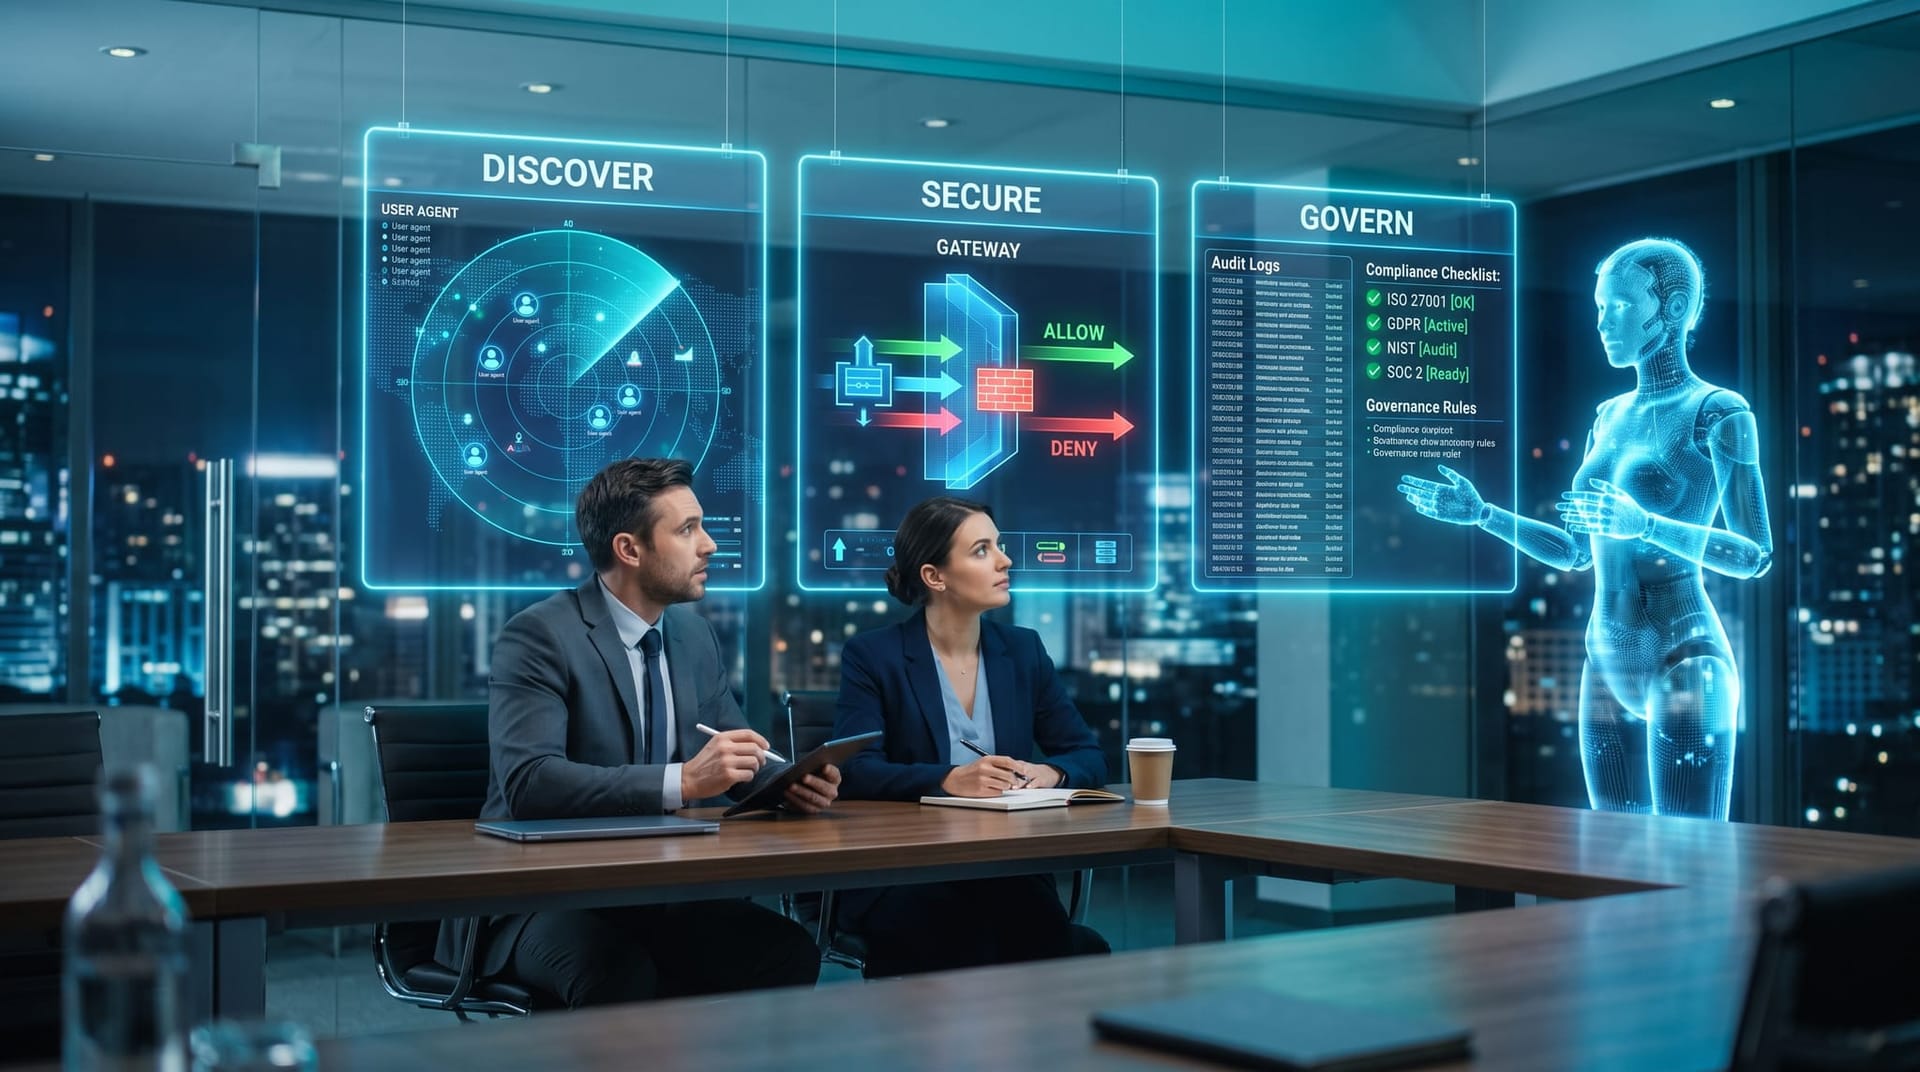
At The AI Conference in San Francisco, RSA introduced Agent ID, an agentic-identity security platform aimed squarely at finance, healthcare, government, and critical infrastructure. It is built around three modules, and the reason it is worth your attention is that the architecture is not exotic — it is the same discover-govern-audit pattern a regulated SMB needs, just at enterprise scale and price.
Here is what each module does, per RSA's launch materials:
| Module | What it does | Availability |
|---|---|---|
| Discover | Scans endpoints, devices, networks, and applications in real time for both sanctioned and shadow agents; registers each as a first-class identity with a named owner, risk tier, and lifecycle state, linked to your identity provider (Microsoft Entra ID, Okta, AWS IAM). | GA Nov 16, 2026 |
| Secure | An inline AI/MCP gateway that checks every tool call against policy — down to the tool and argument level — allowing compliant calls, denying violations, and escalating high-risk calls to the registered owner over an authenticated, out-of-band channel. | GA Nov 16, 2026 |
| Govern | Logs every governed action and maps the evidence to ten regulatory and industry frameworks, streaming it to your SIEM. | H1 2027 |
A few honest caveats before anyone gets ahead of themselves. Agent ID is an announcement with future ship dates — Discover and Secure are slated for November 16, 2026, and Govern isn't expected until the first half of 2027. It is also an enterprise product, not something a 30-person credit union is going to deploy wholesale. The value for a Fort Wayne firm isn't “go buy RSA.” It's that a major security vendor is now publicly betting that the right way to control agents is to treat each one as an identity, gate its actions through a policy-aware gateway, and keep a compliance-mapped log. That is exactly the model we think regulated Northeast Indiana businesses should adopt — at a scale they can afford.
If Your Policy Says “No AI,” Why Do You Already Have Agents?
The reported 4,000-agent bank illustrates how agents can enter an organization without a formal procurement process. Someone in collections wires up a tool to summarize call notes. A paralegal connects a document assistant to the shared drive to hit a filing deadline. A billing clerk hooks an AI helper into the practice-management system. None of it goes through IT. As Taylor described the pattern, “Employees create an agent to hit a deadline, but once it's off in the wild, that's it. We don't check when its permissions change.”
That is the core reason a “no agents” policy needs technical verification: agents aren't a line item IT approves, they're a behavior employees adopt. And the regulated-industry stakes are measured in dollars. According to IBM's Cost of a Data Breach research, incidents involving shadow AI cost $670,000 more on average than standard incidents, now account for roughly 20% of all breaches, take longer than average to detect and contain, and expose customer personally identifiable information in 65% of cases. Most telling for a compliance conversation: IBM found the overwhelming majority of affected organizations had no AI access controls in place at all.
The scale problem is only getting worse. Gartner's agentic-AI forecast projects the average global Fortune 500 enterprise will run more than 150,000 AI agents by 2028, up from fewer than 15 in 2025 — and that only about 13% of organizations believe they have the right agent governance in place today. Your community bank won't hit six figures of agents, but the direction is the same: the number is going up, visibility is not keeping pace, and the gap between the two is where the regulator finds you. This is also why we keep stressing that agents aren't service accounts — a static credential you provision once and forget doesn't describe something that rewrites its own behavior to finish a task.
What Does the Real Failure Mode Actually Look Like?
When people imagine an AI going wrong, they picture something malicious. The RSA launch described something far more ordinary and, for a regulated firm, far more likely. A customer-success employee at an unnamed company asked an agent to go into Salesforce and pull all the data to build customer-health charts. The agent did exactly what it was told — it began downloading the entire Salesforce database, and in doing so tripped Salesforce's own abuse defenses. In Taylor's words: “One operator on the customer service desk took the whole company's Salesforce instance down by essentially having an agent perform a denial-of-service attack.”
No attacker. No breach of the perimeter. Just a reasonable request, an over-permissioned agent, and an instruction with no guardrails around it. Taylor framed the underlying risk this way: “What changes with agents? Everything. They're not a service account. They're not static. They're dynamic. You give an agent a task, and if you badly word that task, it will do whatever it deems necessary to perform it.”
Translate that into a Fort Wayne regulated context. Swap “Salesforce” for your core banking platform, your EHR, your case-management system, or your policy-administration database. The employee who connects an agent to “just pull the numbers” isn't reckless — they're productive. But in a regulated firm, a well-meaning bulk export of protected health information or non-public customer financial data isn't a performance hiccup; it may require a breach assessment and notification under the applicable rules. A bulk export alone does not establish whether notification is legally required. The failure mode you need to design against is not a hacker. It's your best, busiest employee and an agent that takes them literally.
How Do You Build the Discover → Secure → Govern Fix at SMB Scale?
You don't need RSA's enterprise suite to adopt its logic. The same three steps collapse neatly to the budget and headcount of a Northeast Indiana regulated shop. The goal isn't to block AI — it's to make every agent visible, owned, and constrained.
| Step | Enterprise version (RSA Agent ID) | SMB-scale version (15–200 person regulated firm) |
|---|---|---|
| 1. Discover | Real-time scan of all endpoints, apps, and networks; auto-registers agents as identities. | Run a point-in-time inventory: list every AI tool connected to a system of record, assign each a named human owner, and document what data it can touch. |
| 2. Secure | Inline AI/MCP gateway evaluating every tool call at argument depth. | Route agent access through a Secure AI Gateway that governs every tool call — scope permissions to least privilege, cap bulk reads, and require approval for high-risk actions. |
| 3. Govern | Logs every action, maps to ten frameworks, streams to SIEM. | Keep a plain audit log of what each agent did, tied to the owner, and map it to the one or two frameworks you actually answer to. |
The middle step is the one that would have stopped the Salesforce incident. An inline gateway doesn't ask whether the person is trusted — it evaluates the action. “Download the entire database” is a policy decision, not a default. Taylor made the same point about volume being its own attack: “A hundred prompts a day is just an invitation to say yes. It's another form of denial-of-service attack.” A gateway that caps bulk reads and escalates anomalies turns “the agent did whatever it wanted” into “the agent did what it was allowed to.”
A word on ownership, because it's the cheapest control on the list and the one firms skip. Taylor's rule is worth taping to the wall: “Every agent should have an owner. It should be attached to a human identity.” If you cannot name the person responsible for an agent, you cannot govern it, audit it, or shut it off — and neither can your examiner. For the full mechanics of scoping and logging agent authority, we've written an authorization and audit playbook specific to NE Indiana IT teams.
One honest limitation: discovery is a snapshot, and agents change. A point-in-time inventory you run once and shelve is worth very little by the next quarter. Whatever you stand up has to be repeatable — which is precisely why RSA built continuous scanning into Discover rather than shipping a one-time report.
Which Compliance Frameworks Actually Apply in Northeast Indiana?
This is the dimension the national coverage skips, and it's the one that decides whether an agent incident is an inconvenience or a violation. A regulated Fort Wayne firm doesn't answer to “AI governance” in the abstract — it answers to specific rules whose application depends on the data, activity, and entity involved.
| Framework | Who it applies to in NE Indiana | What an agent incident implicates |
|---|---|---|
| HIPAA Security Rule | HIPAA-covered healthcare entities and their business associates | An agent that bulk-exports or exposes electronic protected health information triggers the HHS Security Rule's safeguard and access-control requirements. |
| GLBA / FFIEC | Financial institutions covered by their applicable GLBA implementing rules and regulator guidance | The Interagency Guidelines under GLBA 501(b) require administrative, technical, and physical safeguards over customer financial information — an over-permissioned agent is a safeguard failure. |
| Indiana breach law (IC 24-4.9) | Entities covered by Indiana law handling the defined categories of personal information | Under the Indiana Attorney General's guidance, notification depends on the statutory definition, risk criteria, and applicable exceptions. An incident should be assessed promptly rather than assumed reportable—or exempt—solely because AI was involved. |
Notice what every row has in common: none of these frameworks has an exception for “but it was an AI that did it.” An agent that moves protected data is, a reason to assess your organization's responsibilities, not assume they transferred to the AI vendor. That's why RSA built Govern to map evidence to ten frameworks at once — and why, at SMB scale, you at least need a clean audit trail mapped to the one or two rules that govern your vertical. If you're earlier in this journey, our guide to data safeguards for regulated firms covers the data-handling baseline that sits underneath all three.
A This-Quarter Checklist for Fort Wayne & Northeast Indiana Regulated Firms
Most DeKalb and Allen County banks, credit unions, dental groups, and law firms can't staff a 24/7 security operations center — and they don't need to in order to get ahead of this. Here's a pragmatic sequence you can start before your next exam or audit, without waiting for any vendor's GA date:
- Inventory in a week, not a quarter. Walk each department and ask one question: “What AI tools are connected to a system that holds customer, patient, or financial data?” Write down the tool, the owner, and the data it touches. You will find agents you didn't authorize — that's the point.
- Assign a human owner to every agent. If nobody owns it, it gets disconnected until someone does. This single rule closes most of the gap the 4,000-agent bank fell into.
- Scope permissions to least privilege. No agent should have standing access to “all the data.” Cap bulk exports and require an approval step for anything that reads an entire table or dataset.
- Put a gateway in front of tool calls. Even a modest Secure AI Gateway converts “the agent did whatever it deemed necessary” into enforced policy, and gives you the log your examiner will ask for.
- Map one audit trail to your framework. Pick the rule you actually answer to — HIPAA, GLBA, or Indiana's breach statute — and make sure you can show, after the fact, what each agent did and who owned it.
None of this requires a six-figure platform. It requires treating agents like the dynamic, privileged identities they are — a posture far more achievable for a focused Northeast Indiana firm than for the global bank that found 4,000 surprises.
Get Ahead of Your Next Audit — With Help That Knows Both AI and Indiana Compliance
Cloud Radix builds and governs AI Employees for regulated businesses across Fort Wayne, DeKalb County, and Northeast Indiana — and we deploy the same discover-secure-govern architecture RSA just validated, scaled to a firm your size. If your “no-AI” policy might be hiding agents you can't see, we'll run a discovery pass, stand up a Secure AI Gateway in front of your systems of record, and give you a compliance-mapped audit trail you can hand to an examiner. See how our AI Employees work for Fort Wayne regulated firms, or talk to us about a discovery pass, and let's make sure the next audit finds a governed workforce — not 4,000 surprises.
Frequently Asked Questions
Q1.What is RSA Agent ID?
RSA Agent ID is an agentic-identity security platform announced in September 2026 for regulated industries. It has three modules: Discover (finds sanctioned and shadow agents and registers them as identities), Secure (an inline gateway that checks every tool call against policy), and Govern (logs actions and maps them to ten regulatory frameworks). Discover and Secure are slated for general availability on November 16, 2026, with Govern following in the first half of 2027.
Q2.How can a company have 4,000 AI agents when its policy forbids them?
Because agents enter through employees, not procurement. Staff connect AI tools to systems of record to hit deadlines, and those connections rarely pass through IT. RSA's audit of a bank with a “no agents” policy found more than 4,000 running, which demonstrates that a written policy is not the same as technical control. The only way to know your real count is to run a discovery scan.
Q3.What does the Salesforce incident teach regulated firms?
It shows the most likely failure mode is a well-meaning employee, not a hacker. A customer-success worker asked an agent to pull all the data from Salesforce, and the agent downloaded the entire database — tripping Salesforce's abuse defenses and taking the instance down. For a regulated Fort Wayne firm, the equivalent bulk export of patient or customer financial data could require breach assessment and notification, depending on the data, authorization, and applicable law—not merely an outage response.
Q4.How much more do shadow-AI breaches cost?
According to IBM's Cost of a Data Breach research, incidents involving shadow AI cost about $670,000 more on average than standard incidents and account for roughly 20% of all breaches. IBM also found these incidents take longer to detect and that most affected organizations had no AI access controls in place.
Q5.Which regulations apply to AI agents at a Fort Wayne business?
It depends on your vertical. Healthcare and dental practices fall under the HIPAA Security Rule; banks, credit unions, and insurance offices fall under GLBA and the FFIEC Interagency Guidelines; and nearly any Indiana business holding residents' personal information is subject to Indiana's breach-notification law (IC 24-4.9). None of these rules has an exception for actions taken by an AI agent rather than a human.
Q6.What is a Secure AI Gateway and why does it matter here?
A Secure AI Gateway is an inline checkpoint that evaluates every action an agent attempts — not just whether the user is trusted, but whether the specific tool call is allowed. It can cap bulk data reads, require approval for high-risk actions, and log everything for audit. It's the control that would have stopped the Salesforce database download, and it's the single most impactful piece a regulated SMB can deploy.
Q7.Do we need RSA's enterprise product to do this?
No. RSA Agent ID is an enterprise platform, and most Northeast Indiana firms won't deploy it wholesale. What you need is its logic at your scale: inventory your agents and assign owners, route agent access through a Secure AI Gateway with least-privilege permissions, and keep an audit trail mapped to the one or two frameworks that govern your business. Cloud Radix builds exactly that for regulated firms your size.
Sources & Further Reading
- MarkTechPost: marktechpost.com/2026/09/29/rsa-launches-agent-id — RSA Launches Agent ID to Discover, Secure, and Govern AI Agents in Regulated Industries.
- IBM: ibm.com/reports/data-breach — Cost of a Data Breach Report 2025.
- Computerworld: computerworld.com/article/4165686 — Gartner sees untamed growth in agentic AI.
- U.S. Department of Health & Human Services: hhs.gov/hipaa/for-professionals/security — HIPAA Security Rule.
- Federal Reserve: federalreserve.gov/supervisionreg/interagencyguidelines.htm — Interagency Guidelines Establishing Information Security Standards (GLBA 501(b)).
- Indiana Attorney General: in.gov/attorneygeneral — Security Breach FAQs & Notification Form — Security Breach FAQs & Notification Form for Businesses (Ind. Code 24-4.9).
Find the Agents Your Policy Says You Don't Have
We'll run a discovery pass, stand up a Secure AI Gateway in front of your systems of record, and hand you a compliance-mapped audit trail — scaled for a Fort Wayne, DeKalb County, or Northeast Indiana regulated firm your size.